Cyber Blankitt: digital safety news and guides for individuals, families, and small retail businesses
Most scams are stopped by three habits, not by software.
Lock your email, use one password per site, and treat anything urgent, secret and asking you to pay as the scam it is. Everything here comes back to those. Pick the one that is yours.
- 28 readers
- 37 stories since 30 June 2026, every one linked to its source
- One email a week, one thing to do
Protect my money and accounts Three habits stop most of it. Start with your email.
Start here
Do one thing: Lock your email first, use unique passwords, and never act on a link in a message.
- Turn on a passkey or 2FA for your email and bank before anything else.
- Use a password manager so every login is unique, so one breach can’t cascade.
- Check what’s leaked about you, then change those passwords.
- Got a message that’s urgent, secret and asks you to pay? That triad is the scam.
This week
- Get apps from the maker, not an ad Fake Claude installers in Google ads use Bing redirects to send Mac users to a page that tells them to paste a command into Terminal. A sponsored result can look trusted, so get apps only from the maker’s own site. BleepingComputer · Oct 2026
- Report nuisance calls; the regulator acts on them Complaints to the ICO about automated nuisance calls rose from 1,374 in July to 3,684 in September, a five-year high. Reporting suspicious calls and texts helps the regulator act. ICO · Oct 2026
- Walk away from easy payment-handling jobs The leader of a 15,000-strong money mule network pleaded guilty after recruiting people through fake job emails. Easy “work from home” jobs handling payments can make you an unwitting money launderer, so walk away. BleepingComputer · Oct 2026
Keep the kids and the household safe Set the controls once, then keep talking.
Start here
Do one thing: Set the controls once, then have the conversation. Tech plus talking beats either alone.
- Use child accounts, content filters, and screen time limits on every device and the router.
- Lock down a child’s first phone before you hand it over (a 10 minute job).
- Teach the red flags: secrecy, “you’ve won, pay to claim”, and any link that leads to a payment.
- Agree family rules and a “check with me first” habit for links and payments.
This week
- Report nuisance calls; the regulator acts on them Complaints to the ICO about automated nuisance calls rose from 1,374 in July to 3,684 in September, a five-year high. Reporting suspicious calls and texts helps the regulator act. ICO · Oct 2026
- Walk away from easy payment-handling jobs The leader of a 15,000-strong money mule network pleaded guilty after recruiting people through fake job emails. Easy “work from home” jobs handling payments can make you an unwitting money launderer, so walk away. BleepingComputer · Oct 2026
- Health data breached; expect convincing follow-up scams Heart-monitor maker iRhythm told at least 360,000 people their details were taken in a June breach, mostly US patients. Health-linked details can fuel convincing scam calls, so verify any caller. The Record · Oct 2026
Keep my shop trading Three things, in order, and most attacks bounce off.
Start here
Do one thing: Get Cyber Essentials, turn on MFA everywhere, and stop scammers spoofing your email.
- Start Cyber Essentials now. It’s becoming a condition of supplying larger firms.
- Enable MFA on every cloud service (or you’ll fail certification).
- Protect your shop’s email with DMARC so criminals can’t spoof your domain.
- Train staff on invoice fraud and phishing; vet your IT supplier (the M&S lesson).
This week
- Using SonicWall SMA1000? Patch today A max-severity flaw in SonicWall SMA1000 remote-access gateways (advisory SNWLID-2026-0017) is now being exploited. It affects SMA1000 6210/7210/8200v only, so if you use one, patch now. BleepingComputer · Oct 2026
- Ask your IT supplier about AhsayCBS Unpatched flaws in AhsayCBS backup software are being exploited, and the latest version is also affected. If your IT supplier runs it, ask whether its admin page is locked down. BleepingComputer · Oct 2026
- Qilin arrest helps, but keep backups and patching Germany has arrested an alleged core member of the Qilin ransomware group after extradition from Japan. Qilin has hit 2,350+ organisations in 62 countries and is not shut down, so backups and patching still matter. BleepingComputer · Oct 2026
Tools
Seven short emails, one a day, one thing each. Then the weekly.
Sign up and the first arrives when you confirm: lock your email. Then one password each, what has already leaked, the three words every scam uses, the family, the shop, and what to do when it goes wrong. Ten minutes each. After that, one email a week, and reply to any of them.
We send a confirmation first; nothing arrives until you press it. Unsubscribe any time.
This week, in one line 12 October 2026
This issue with every story and source → All issues · Archive
Who writes this
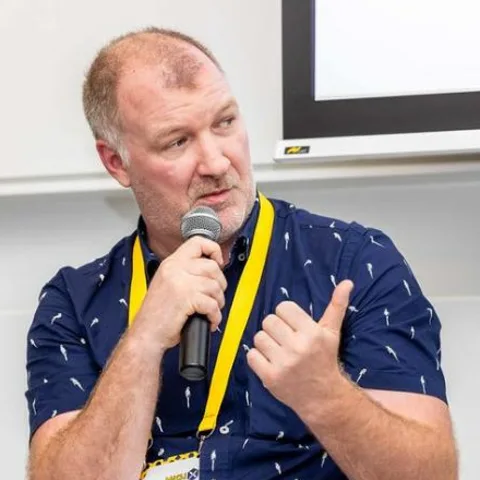
I'm Simon Edwards. I've done security in the military, in local and central government, in banking and insurance, and now in retail. The threats changed every time; the three habits that stop most of them never did. Cyber Blankitt is the one email a week I'd want my own family and the shops I know to get: what happened, where it came from, and the one thing to do about it. Free. How it makes money is on the disclosure page.